DevOps & CI/CD
Envless
End-to-end encrypted environment variable and secrets management for developers and teams
Manages encrypted environment variables and secrets across teams with client-side AES-256 encryption, typed SDKs, CLI tools, and version control.
Overview
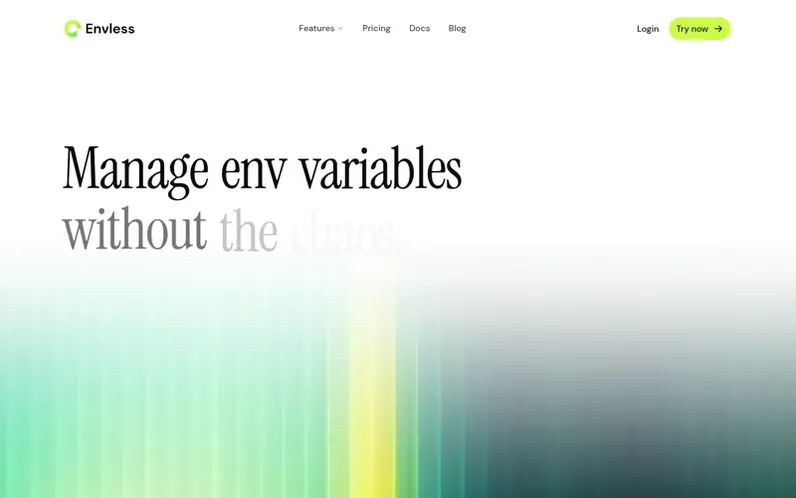
A look at envless.cloud
Envless is an end-to-end encrypted secrets manager that replaces .env files. Values are encrypted with AES-256-GCM on your machine before reaching the servers, so only ciphertext is stored. It provides a CLI with 24 commands, typed SDKs for TypeScript, Python, Ruby and PHP, a cloud dashboard, and a public REST API with 80 operations. The platform includes team collaboration features with role-based access control across 45 permissions, version history with rollback, and workspace activity tracking. Developers can inject secrets into processes at runtime using the CLI, integrate with frameworks like Next.js and Vite, and manage environments across local, staging, production and CI systems with a single command.
Feature notes
- Team collaboration with attributed change history
Pricing
Free: 1 product, 1 project, 2 environments per project with unlimited encrypted variables. Dev: $5/month for 3 products, 3 projects, 3 environments per project. Team: $25/month for 15 products, 15 projects, 15 environments per project and 10 team members. Enterprise: $50/month for unlimited products
Compare and explore
FAQ
- Are environment variables end-to-end encrypted on every plan?
- Yes. Every variable value is encrypted on your device before reaching servers, so neither Envless nor any third party can read it. End-to-end encryption is the default on every plan, including Free, with no setting to turn it off.
- How does Envless keep my secrets safe?
- Secrets are encrypted client-side and only ciphertext is stored, never plaintext values. All traffic is encrypted with TLS, sign-in is passwordless to prevent credential compromise, an optional TOTP second factor can be enabled, and encrypted copies are stored redundantly for data resilience.
- How do I sign in to Envless?
- Sign-in is passwordless using a one-time code emailed to you, a magic link, or Google or GitHub OAuth. You can enable an optional TOTP second factor from your account page using any authenticator app. There is no account password to phish or leak, and decryption requires the workspace passphrase that servers never hold.
- Do I need a credit card to get started?
- No. The Free plan includes 1 product, 1 project and 2 environments with unlimited encrypted variables, plus the API, SDK, CLI and MCP server, with no credit card required. You only add a payment method when upgrading to Dev, Team or Enterprise plans.
- Can my whole team collaborate securely?
- Yes. Team plan includes 10 team members and Enterprise has no seat limit, with role-based access control across 45 permissions. Private products stay visible only to named members, and full version history with rollback plus attributed change history on every variable is available.
Leave a review for Envless
No reviews of Envless yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
Envless has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link: not on this free listing (its website link is nofollow)
Comparable tools
- BROKADR 4 · 0 community votes
- RenDR 3 · 0 community votes
- HW ConnectorDR 0 · 0 community votes
- opsDR 27 · 0 community votes