Security, Privacy & Compliance
LeakCheck
Free scanner to find leaked keys, open tables and exposed files in your live app and code
LeakCheck scans your live app and public GitHub repos for leaked API keys, open databases, exposed files, and security misconfigurations.
Overview
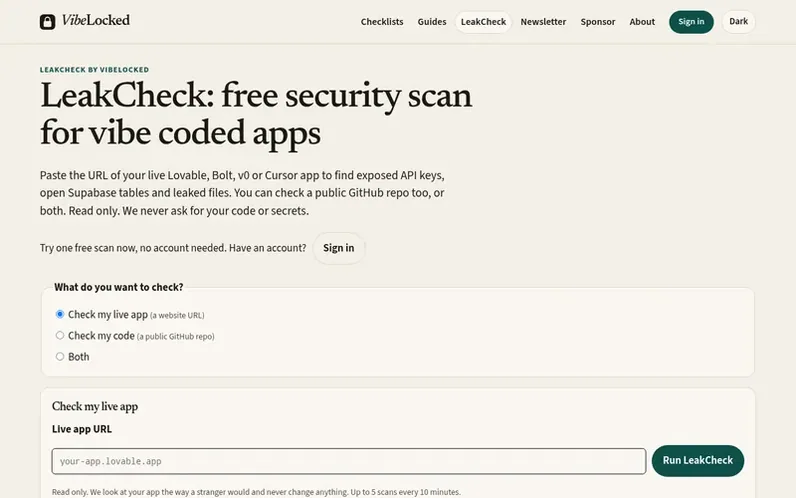
A look at vibelocked.com
LeakCheck is a free, read-only security scanner for developers building with AI coding tools. It checks your live app by URL and scans public GitHub repositories for leaked API keys from services like OpenAI, Anthropic, Stripe, AWS, and others, plus open database tables, misconfigurations in Firebase and Supabase, and other security exposures.
The live app check scans for stack fingerprints, CVE vulnerabilities, Firebase and Supabase misconfigurations, GraphQL introspection, TLS certificate issues, and email spoofing risks via SPF, DMARC, and DKIM records. The code check examines files in public repos for hardcoded secrets and generic secret patterns, skipping node_modules and large files.
LeakCheck Free offers one preview scan without an account. After signing in free, users can run up to 5 scans every 10 minutes and see full details for the top 2 findings. LeakCheck Pro, at $15 a month or $12 a month billed yearly, automatically rescans apps after every deploy and on daily, weekly, or monthly schedules, stores scan history, sends alerts via email, Slack or Discord, and monitors up to 5 apps.
Feature notes
- Live app security scanning by URL
- Public GitHub repository code scanning
- API key and token detection
- CVE vulnerability scanning
- Email spoofing protection checks
- Alerts via email, Slack or Discord
- Markdown reports and README badges
- Monitor up to 5 apps continuously
- Scan history and score tracking
Pricing
Pricing model: Freemium
LeakCheck Free: US$0. LeakCheck Pro: $15 USD a month, or $12 USD a month billed yearly ($144 a year). Cancel any time.
Compare and explore
FAQ
- What does LeakCheck scan for?
- LeakCheck scans live apps for leaked API keys, open database tables, CVE vulnerabilities, Firebase and Supabase misconfigurations, GraphQL introspection, TLS certificate issues, and email spoofing risks. Code scans check public GitHub repos for hardcoded secrets from services like OpenAI, Anthropic, Stripe, AWS, and others.
- What should I do if LeakCheck finds a leaked secret?
- Rotate the key at the provider first, then remove it from code and git history. Deleting the line is not enough once it was pushed or deployed.
- Does LeakCheck require access to my code or secrets?
- No. LeakCheck is read-only and never asks for your code or secrets. For live app scans, it uses GET, HEAD, and OPTIONS requests only. For code scans, it reads files from GitHub's public API without needing access to private repositories.
- How often does LeakCheck Pro rescan my apps?
- LeakCheck Pro rescans seconds after every deploy via a deploy hook, and also on daily, weekly, or monthly schedules that you set per app. Rescan frequency can be switched on or off for each app.
Leave a review for LeakCheck
No reviews of LeakCheck yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
LeakCheck has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Comparable tools
- VigilanceDR 5 · 0 community votes
- ctlogs.devDR 38 · 0 community votes
- KeyEnvDR 8 · 0 community votes
- depproofDR 14 · 0 community votes