Security, Privacy & Compliance
KeyEnv
Secure secrets management for teams with encrypted environment variables and audit logs
KeyEnv is a secrets management platform that encrypts environment variables, enables secure team collaboration, and provides audit logging for development
Overview
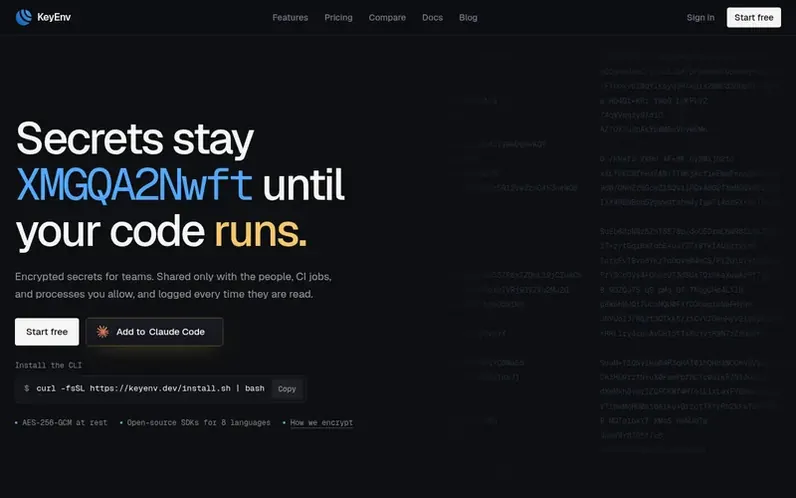
A look at keyenv.dev
KeyEnv helps teams securely store, sync, and share environment variables across development workflows. Secrets are encrypted with AES-256-GCM before storage and never left unencrypted on disk. The platform replaces insecure practices like sharing .env files via Slack or email, offering team collaboration with role-based access control per environment, complete audit logs of all secret reads, and CLI-first automation for developers, CI/CD pipelines, and AI agents. It supports database credential rotation, hardcoded secret scanning, and integrates with popular development tools.
Feature notes
- AES-256-GCM encryption at rest
- Run without .env file on disk
- Role-based access per environment
- Service tokens for CI/CD
- Database credential rotation for PostgreSQL and MySQL
- Secret scanning for hardcoded keys
- SDKs for 8 languages and CI/CD platforms
- Environment inheritance and overrides
- Complete audit logs of all secret access
- AI agent integration for Claude, Cursor, Codex
Pricing
Pricing model: Freemium
Free: up to 3 projects, 100 secrets per environment, CLI access. Team: $4 per user per month (or $3.33 per user per month with annual billing, $40 per user per year, saving 17%). Enterprise: custom pricing with SSO/SAML, custom integrations, SLA and dedicated support, on-premise option.
Compare and explore
FAQ
- What is KeyEnv?
- KeyEnv is a secrets management platform that helps teams securely store, sync, and share environment variables across development workflows. It replaces insecure practices like sharing .env files via Slack or email.
- How are secrets encrypted?
- Secrets are encrypted using AES-256-GCM before storage. Each secret has a unique initialization vector (IV). The encryption key is securely managed and never exposed.
- Can KeyEnv employees see my secrets?
- No. Secrets are encrypted at rest with keys that KeyEnv employees cannot access. The service follows zero-knowledge principles for secret storage.
- What happens if KeyEnv is down?
- The CLI caches secrets locally encrypted, so your applications continue working. Once connectivity is restored, secrets sync automatically.
- Do you offer annual billing?
- Yes. Choose annual billing to save 17% — just $3.33 per user per month billed annually ($40 per user per year) instead of $4 per user per month.
Leave a review for KeyEnv
No reviews of KeyEnv yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
KeyEnv has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Comparable tools
- VigilanceDR 5 · 0 community votes
- ctlogs.devDR 38 · 0 community votes
- depproofDR 14 · 0 community votes
- OrionAlertsDR 0 · 0 community votes