Cybersecurity
SniffPup
Security scanner that finds leaked API keys and exposed files in AI-built apps
SniffPup is a passive security scanner for web apps built with AI tools like Lovable, Bolt and Cursor. It checks publicly visible code for leaked API keys
Overview
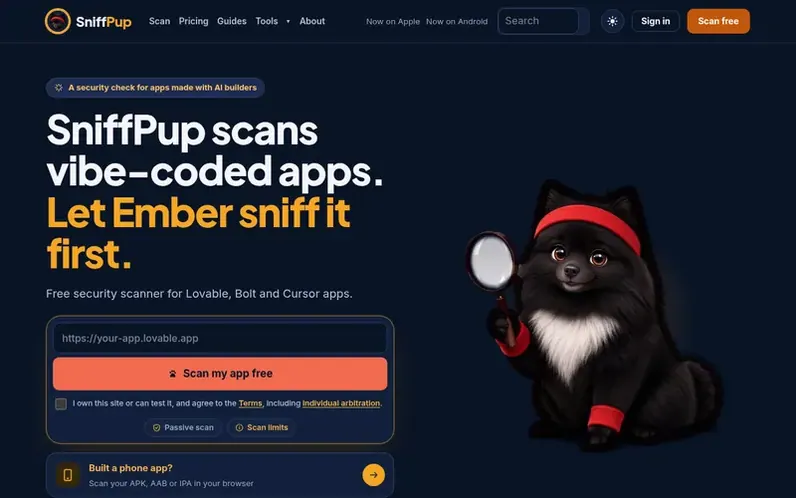
A look at sniffpup.com
SniffPup is a passive, read-only security scanner that checks web apps from the outside, the way a visitor's browser would see them. It scans for leaked API keys in JavaScript and inline scripts, public .env and .git files, exposed source maps, missing security headers, cookie flag issues, HTTPS problems, outdated JavaScript libraries, and what AI crawlers like GPTBot can access. The free scan provides every issue it finds by severity; paid plans add detailed fix prompts for Lovable, Cursor, Bolt and Claude Code, plus scheduled rescans and alerts.
The tool is designed specifically for apps built with AI builders, which ship fast and can accidentally leave secrets or open databases exposed. Every finding includes a plain-English explanation. Paid plans include an AI rules file that tells your coding tool not to repeat the same issues, and verified site owners can run deep checks on Supabase and Firebase databases to see what data a stranger can read.
SniffPup is made by Ember and Saru LLC, a small independent company in Charlotte, North Carolina. Payments are handled through Stripe. The service emphasizes that it is passive and never logs in, sends attack payloads, or misuses any secret it finds.
Feature notes
- Leaked API key detection in JavaScript and inline scripts
- Public .env, .git and other sensitive file discovery
- Security headers validation
- Source map exposure detection
- HTTPS certificate validation
- Outdated JavaScript library detection
- AI crawler visibility check
- Database exposure testing for verified owners
- AI rules file generation to prevent future issues
Pricing
Pricing model: Freemium
Free scan; Full Fix Report $9 one-time; Solo $7/month or $70/year; Starter $15/month or $150/year; Pro $29/month or $290/year; Ultimate $49/month or $490/year. Yearly plans include 2 months free.
Compare and explore
FAQ
- Is it safe to scan my app?
- Yes. Free scans are passive. SniffPup loads your page and the JavaScript it ships like a normal browser, plus a short fixed list of well-known paths such as /.env and /.git/config. It never logs in, never sends attack payloads and never uses a secret key it finds.
- Do you store the secrets you find?
- No. Findings are stored with secrets masked, never the full value. For Pro database checks, only whether a table or bucket is readable and its row count are stored, never row contents.
- What do I get for $9?
- Every finding for one app with a plain-English explanation and a copy-paste fix prompt for Lovable, Cursor, Bolt and Claude Code, plus 30 days of free re-scans to check your fixes. You pay once with no account or subscription.
- Can I cancel or get a refund?
- You can cancel a subscription bought on the website anytime from the billing portal; it ends at the end of the billing period. Purchases made in the app are cancelled and refunded through the store you paid. All sales are final except where required by law or if charged in error.
- Does a clean result mean my app is secure?
- No. A passive scan catches common, costly mistakes quickly, but it is not a penetration test or a code audit. A clean report means no issues were found in the checks run, not proof of security.
Leave a review for SniffPup
No reviews of SniffPup yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
SniffPup has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Comparable tools
- Bugcrowd0 community votes
- DivoltDR 18 · 0 community votes
- StealthMoleDR 33 · 0 community votes
- mlab.shDR 26 · 0 community votes