Cybersecurity
SecuredAI
AI security for chatbots, RAG systems, and agentic workflows
SecuredAI provides unified security services covering LLM red teaming, runtime defense, and identity governance across customer-facing chatbots, internal RAG
Overview
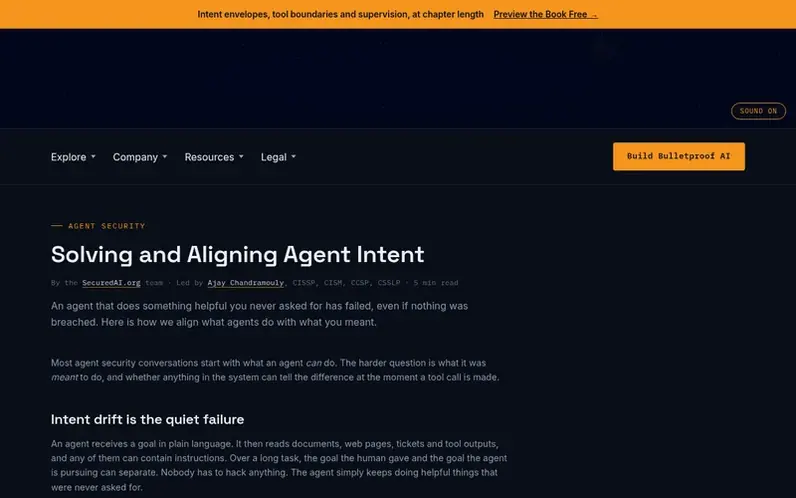
A look at securedai.org
SecuredAI is a boutique AI security firm that combines red team assessment, runtime guardrails, and identity governance across three AI threat surfaces: customer-facing chatbots, internal RAG systems, and agentic AI workflows. Rather than stitching together multiple vendors, SecuredAI runs all three disciplines under one team and methodology. The firm specializes in aligned agent intent through declared intent envelopes enforced at every tool call, with human approval for high-impact actions. SecuredAI also publishes the open-source Zero-Trust Agent Reference Architecture and an intent envelope specification.
Feature notes
- Intent envelope specification with open JSON Schema
- Multi-turn jailbreak and injection testing across web, mobile, and voice
- Deterministic execution boundary enforcing tool allowlists
- Human-in-the-loop escalation for high-impact actions
- Identity and credential separation per agent
- Supervisor check for independent action validation
- Free AI attack surface assessment tool
- Findings mapped to OWASP, MITRE ATLAS, and NIST AI RMF
Compare and explore
FAQ
- What is an intent envelope?
- An intent envelope is a written, versioned artifact that declares what an AI agent is for, which tools it may call, which data it may touch, who it may send anything to, and what it may spend. The envelope is written before the agent runs and checked at every tool call.
- Do I need special hardware to secure AI agents?
- No special hardware is required. The boundary must live outside the model with separated identity and credentials, a deterministic execution boundary, an independent supervisor check, and human escalation. Hardware watchdogs can add isolation but the same six-layer approach can be enforced in software.
- Is the Zero-Trust Agent Reference Architecture a product?
- No, the Zero-Trust Agent Reference Architecture is free to read with no signup. Implementing it correctly is the work.
- What does SecuredAI do?
- SecuredAI is a boutique AI security firm. We combine red team assessment, runtime guardrails, and identity governance across three surfaces, customer-facing chatbots, internal RAG systems, and agentic AI workflows, under one team and one methodology.
- How is securing a chatbot different from securing RAG or an AI agent?
- Each surface fails differently. Chatbots are attacked through conversation, internal RAG through the permissions and content of the documents it retrieves, and agents through the tools and credentials they can use. Testing all three the same way misses the point.
Leave a review for SecuredAI
No reviews of SecuredAI yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
SecuredAI has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Comparable tools
- Bugcrowd0 community votes
- DivoltDR 18 · 0 community votes
- StealthMoleDR 33 · 0 community votes
- mlab.shDR 26 · 0 community votes