Cybersecurity
SaaSecure
100% local codebase vulnerability scanner with zero cloud uploads
Desktop SAST tool that scans codebases for OWASP Top 10 vulnerabilities offline using a Rust engine, with no cloud uploads or telemetry.
Overview
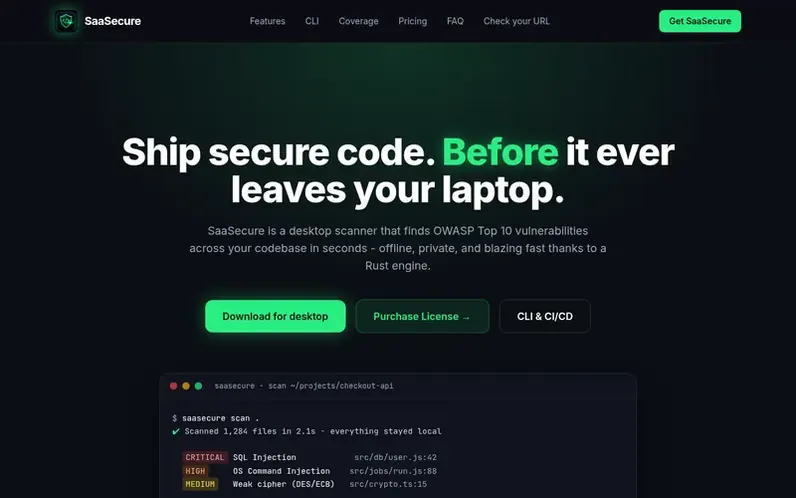
A look at saasecure.dev
SaaSecure is a local static application security testing (SAST) tool that identifies OWASP Top 10 vulnerabilities in codebases by scanning JavaScript, TypeScript, Python, Java, PHP, Go, and Dart. It runs entirely on your machine using a Rust-powered engine with tree-sitter for abstract syntax tree analysis, detecting flaws like SQL injection, command injection, XSS, SSRF, IDOR, broken cryptography, and hardcoded secrets.
The scanner performs analysis without uploading source code to the cloud, collecting telemetry, or requiring online connectivity after initial activation. It uses device-bound licensing with an automatic 14-day offline grace period. SaaSecure offers a free tier with unlimited scans, Pro tier for individual developers, and Team tier with CLI integration and CI/CD support for small teams.
The product includes a standalone command-line interface (saasecure-cli.exe) for automation in GitHub Actions, GitLab CI, and other pipelines. It supports baseline snapshots to track pre-existing vulnerabilities, differential scanning of modified files, and exports findings to PDF, JSON, and SARIF formats. Licenses are perpetual with optional annual renewals for new rules and features.
Feature notes
- Scans 7 programming languages (JavaScript, TypeScript, Python, Java, PHP, Go, Dart)
- Detects OWASP Top 10 flaws including SQL injection, command injection, XSS, SSRF, IDOR, broken cryptography, secrets
- Rust-powered tree-sitter engine for fast abstract syntax tree analysis
- Taint tracking to reduce false positives
- Export findings to PDF, JSON, and SARIF formats
- CLI tool (saasecure-cli.exe) for CI/CD integration
- Baseline snapshots to track pre-existing vulnerabilities
- Differential scanning of modified files with --since option
- Device-bound licensing with 14-day offline grace period
Pricing
Pricing model: Freemium
Free: unlimited local scans, all 7 languages, severity summary. Pro: $79 one-time (founding price, regular $99), includes full findings with remediation, branded PDF/SARIF/JSON export, device-bound offline license, 1 year of updates; renewal $49/yr. Team: $199 one-time, up to 5 seats, includes CLI a
Compare and explore
FAQ
- Does my source code or scan data ever leave my machine?
- No. SaaSecure runs completely on your machine. Your source code, ASTs, and vulnerability findings never leave your local environment. No cloud processing is used and zero telemetry is collected. The only network calls made are for Ed25519 license validation.
- How does perpetual licensing work?
- Your license is perpetual with no subscription lock-in. You own the software forever. Each purchase includes 1 year of software updates and rule packs. Once the year ends, SaaSecure keeps scanning forever on every version released during your window. Renewal is completely optional.
- Which programming languages and security flaws does SaaSecure detect?
- SaaSecure provides AST-level scanning for JavaScript, TypeScript, Python, Java, PHP, Go, and Dart. It detects critical OWASP Top 10 flaws including SQL Injection, OS Command Injection, Cross-Site Scripting (XSS), SSRF, IDOR, Broken Cryptography, and Hardcoded Secrets.
- How does SaaSecure avoid false positives?
- Unlike regex or grep-based linters that flag naive text matches, SaaSecure uses tree-sitter to build concrete syntax trees and tracks taint sources directly into sink receivers, ensuring you investigate genuine vulnerabilities instead of false alarms.
- Can SaaSecure be used completely offline or in air-gapped environments?
- Yes. SaaSecure verifies cryptographic Ed25519-signed tokens locally on your machine. Once activated, the desktop scanner works fully offline with an automatic 14-day offline grace period between periodic online revalidations, making it ideal for air-gapped or restricted networks.
Leave a review for SaaSecure
No reviews of SaaSecure yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
SaaSecure has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link: not on this free listing (its website link is nofollow)
Comparable tools
- Scam MirrorDR 0 · 0 community votes
- BugcrowdDR 83 · 0 community votes
- DivoltDR 18 · 0 community votes
- StealthMoleDR 33 · 0 community votes