Cybersecurity
liarjs.dev
Browser fingerprint and automation detector that cross-checks JavaScript consistency against network layer signals
A diagnostic tool that analyzes whether a browser is genuine by checking JavaScript consistency, network signals, and human behavior patterns across three
Overview
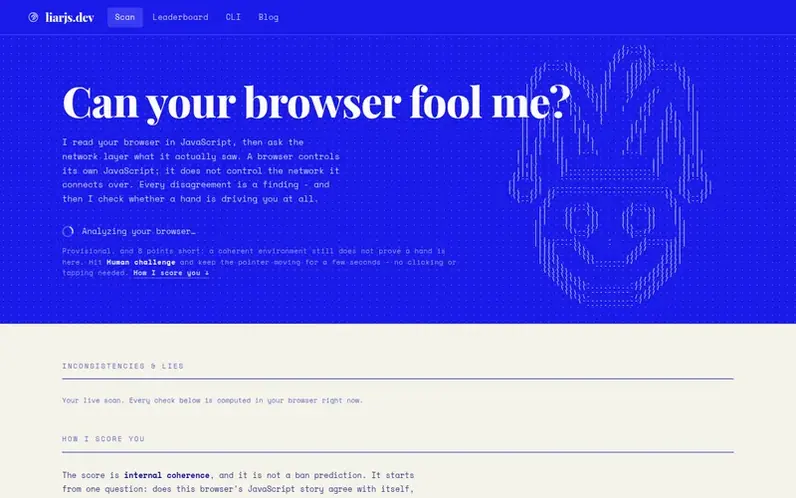
A look at liarjs.dev
liarjs.dev is a browser detection diagnostic that asks whether your browser is genuine and whether a person is actually driving it. It reads your browser's JavaScript properties—canvas, WebGL, WebGPU, audio, fonts, timezone and network data—then cross-checks these against what the network layer actually observed through Cloudflare. Every disagreement between what the browser claims and what the network saw is flagged as a finding.
The tool works on three independent detection axes: Fingerprint checks whether the browser looks like a real device by examining canvas, WebGL, WebGPU, audio, fonts, navigator properties, screen geometry and WebRTC. Network checks whether Cloudflare's observations (TLS version, HTTP protocol, ASN, header shape, IP geography) match the JavaScript story. Automation checks whether a program is driving the browser, first through passive signals like navigator.webdriver and framework residue, then through an active behavioral challenge that measures pointer movement, path curvature and event timing.
The project is both educational and defensive. It helps people understand what modern detectors can observe and lets anti-detect browser developers test their own footprint. A coherent browser story does not prove a human is present, so the tool separates the fingerprint and network scores from the behavioral verification—a score stays provisional until the challenge is completed.
Feature notes
- JavaScript fingerprinting across canvas, WebGL, WebGPU, audio, fonts, navigator and screen
- Network layer analysis via Cloudflare request metadata
- Behavioral challenge to verify human interaction
- Open-source package for CI integration
- Passive automation detection via navigator properties and framework residue
- Cross-layer consistency checking between JavaScript and network signals
Pricing
Pricing model: Free
Compare and explore
FAQ
- Can your browser fool me?
- The tool analyzes whether your browser is genuine by reading its JavaScript properties and cross-checking them against what Cloudflare observed at the network layer. A browser controls its own JavaScript but does not control the network, so any disagreement reveals either spoofing or a coherence failure in anti-detect setups.
- Is a completely unpatched Chrome driven over CDP detectable?
- An unpatched, headed Chrome driven over the DevTools protocol leaves no passive tells, which is why the tool also offers a behavioral challenge. The passive layer may well find nothing, but the challenge exists to verify whether a human is actually present.
- What data does liarjs.dev store or share?
- Nothing about your session is written to a database or shared. The scan runs live in your browser and at the edge as a read-only measurement only.
Leave a review for liarjs.dev
No reviews of liarjs.dev yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
liarjs.dev has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Comparable tools
- Bugcrowd0 community votes
- DivoltDR 18 · 0 community votes
- StealthMoleDR 33 · 0 community votes
- mlab.shDR 26 · 0 community votes