Cybersecurity
Decloak
Web security intelligence platform that scans sites across eight layers and provides audit-ready evidence
Decloak scans websites for security issues across HTTP/TLS, content, network behavior, JavaScript vulnerabilities, third-party scripts, and platform
Overview
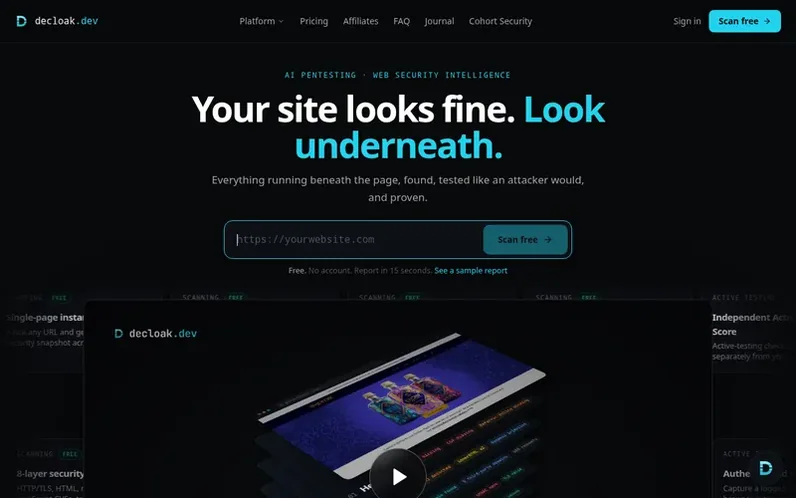
A look at decloak.dev
Decloak is a web security scanner that analyzes websites across eight core layers: HTTP and TLS security posture, static HTML analysis, rendered-page network behavior, JavaScript CVE scanning, tag manager intelligence, third-party domain mapping, vibe-coded platform security for services like Supabase and Lovable, and server software CVE checks. The free tier requires no account and delivers a graded report in 15 seconds. Paid tiers deploy an AI agent to crawl multiple pages, provide AI-written remediation steps specific to each finding, and unlock compliance control mappings for SOC 2, ISO 27001, NIS2, DORA, LGPD, PCI DSS, NIST CSF, and EU CRA. Enterprise tier adds active security testing with sandboxed exploitation confirmation using established tools like sqlmap and dalfox, authenticated scanning via browser session capture, and API endpoint discovery and testing for REST, GraphQL, and SOAP.
Feature notes
- 8-layer security analysis covering HTTP/TLS, HTML, network traffic, JavaScript CVEs, tag managers, third-party supply chain, platform misconfigurations, and server software CVEs
- Single-page instant scan with report in 15 seconds
- JavaScript CVE detection using Retire.js and OSV database
- Third-party domain mapping with threat intelligence checking
- Security score 0-100 and A-F grade calculation
- API endpoint discovery and testing for REST, GraphQL, and SOAP
- AI-written remediation steps specific to each finding
- Subdomain discovery via certificate transparency and common names
- OWASP Top 10 coverage checklist on every report
- Compliance control mapping for NIS2, PCI DSS, and other standards
Pricing
Pricing model: Freemium
Free tier with no account required. Starter from £29/month. Pro from £79/month. Enterprise from £99/month.
Compare and explore
FAQ
- What does Decloak actually check?
- Decloak checks eight core layers: HTTP and TLS security posture, static HTML analysis, rendered-page network behavior, JavaScript CVE scanning, tag manager intelligence, third-party domain mapping, vibe-coded platform security for services like Supabase and Lovable, and server software CVE checks. Enterprise adds active security testing with API endpoint discovery and testing. Starter and up add DNS records, TLS certificate analysis, subdomain discovery, and subdomain takeover detection.
- Do I need an account to scan a site?
- No. The free scan works on any URL without login—just paste it and get a graded, shareable report in about 15 seconds. Creating a free account lets you save scans, view a dashboard across domains, and get a higher daily scan limit.
- What is the difference between the free scan and the paid investigation?
- The free scan runs the core 8 layers once on the single page you submit. Paid tiers deploy an AI agent that keeps crawling and investigating across up to 50 pages on Starter, 200 on Pro or Enterprise, following scripts, source maps, tag manager containers, and linked pages, then produce per-finding remediation guidance.
- Can I scan any website, including ones I don't own?
- Decloak's free, Starter, and Pro scans perform passive, read-only analysis of publicly accessible pages. Enterprise's opt-in Active Security Testing performs safe, non-destructive active probes and requires explicit per-scan consent. Decloak does not attempt exploitation or authentication bypass, and you are responsible for having the right to scan a given target under your local laws and applicable terms of service.
- What is AI Pentesting and how is it different from Active Testing?
- AI Pentesting runs a fixed set of established third-party security tools inside an isolated temporary sandbox to attempt to confirm whether specific findings are genuinely exploitable. This involves real exploitation attempts such as submitting SQL injection or cross-site-scripting payloads, which is materially different from passive analysis and active testing that only detect plausible signals.
Leave a review for Decloak
No reviews of Decloak yet. Run the first inspection.
Reviews are free and are never paid for. Open the reviews
Reviews and notes · Change log · Share the profile · Maker of this product? Claim the profile · Report a fault
Decloak has a free listing. The owner can unlock the full profile with a paid launch for $5:
- Founder story (locked)
- Milestones (locked)
- Demo video (locked)
- Dofollow website link (locked)
Comparable tools
- Bugcrowd0 community votes
- DivoltDR 18 · 0 community votes
- StealthMoleDR 33 · 0 community votes
- mlab.shDR 26 · 0 community votes